
Every day, billions of messages travel across the internet. People send private emails, share financial information, make online purchases, access bank accounts, and exchange personal photographs. Much of this information passes through networks and computer systems that its sender does not directly control. So how can a message remain private while moving through so many different places?
The answer lies in encryption, a technology that transforms readable information into a form that unauthorized people cannot easily understand. Behind this process are encryption algorithms: mathematical methods that use carefully designed rules and cryptographic keys to protect digital information.
Encryption does not make information completely invulnerable to every possible attack. Instead, modern encryption algorithms are designed to make unauthorized access computationally impractical when they are implemented correctly and used with appropriate keys. Understanding how they work reveals why secure messaging, online banking, digital payments, and many other internet services depend on cryptography.

What Is Encryption?
Encryption is the process of converting readable information, known as plaintext, into an unreadable or unintelligible form called ciphertext. The transformation is performed using an encryption algorithm and, in modern systems, a cryptographic key.
The original information might be a short text message, a document, a photograph, or an entire database. Once encrypted, its contents should not be understandable to someone who intercepts the data but does not possess the necessary key.
For example, imagine sending the message:
Meet me at the station at 6 PM.
Without encryption, anyone who gains access to the message may be able to read it. With encryption, the message is transformed into ciphertext that looks like meaningless data. The exact output depends on the algorithm, key, and other inputs used by the encryption system.
The recipient can recover the original message by using the appropriate decryption process.
Encryption therefore provides a mathematical method of protecting information, rather than relying solely on the secrecy of the communication channel. Even if an attacker can see the encrypted data, the security of a properly designed system should prevent that attacker from recovering its contents without the required key.
How Encryption Algorithms Work
Encryption algorithms follow precise mathematical rules. These rules determine how information is transformed, how keys influence the transformation, and how the original data can be recovered by an authorized recipient.
Although different algorithms operate in different ways, the general process follows a few fundamental steps.
1. The Original Message Is Prepared
The process begins with plaintext, which is the information the sender wants to protect. A messaging application might receive ordinary text, while a banking system could be preparing account information or payment details for secure transmission.
The application then passes the information to its encryption system.
Depending on the algorithm, the data may be divided into blocks, processed as a continuous stream, or combined with additional cryptographic information. Some systems also use random values called nonces or initialization vectors to ensure that encrypting the same message twice does not necessarily produce the same ciphertext.
2. The Algorithm Uses a Cryptographic Key
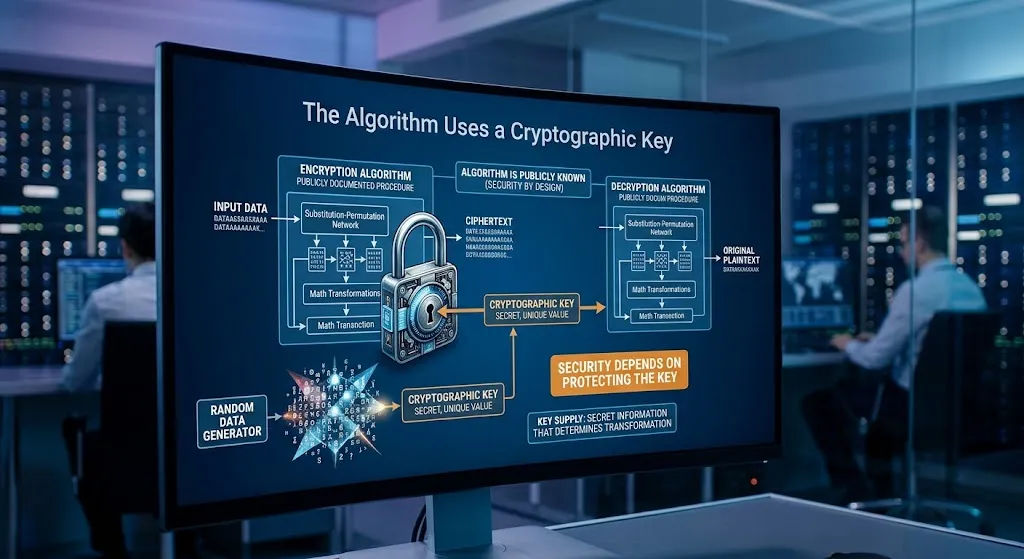
A cryptographic key is a value that controls important parts of the encryption or decryption process. It may be generated from random data or established through a secure key-agreement procedure.
The key is different from the algorithm itself. The algorithm defines the mathematical procedure, while the key supplies secret or controlled information that determines the particular transformation.
This distinction is essential. Modern cryptographic systems generally assume that attackers may know which algorithm is being used. Security should depend on protecting the key, not on hiding the design of the algorithm.
For example, a system might use a publicly documented encryption algorithm that has been extensively studied by security researchers. If an attacker intercepts an encrypted message but cannot obtain the correct key, recovering the original information should remain impractical.
3. Plaintext Becomes Ciphertext
The encryption algorithm combines the message with the key according to its mathematical rules. Depending on the algorithm, the process may involve substitutions, permutations, bitwise operations, modular arithmetic, or other transformations.
Modern encryption algorithms are designed so that the resulting ciphertext reveals very little useful information about the original message.
A person examining the encrypted data should not be able to identify its contents simply by looking for recognizable words or familiar patterns.
The ciphertext can then be stored or transmitted across a network. It may pass through internet service providers, routers, servers, and other infrastructure without exposing the original message to those systems, provided the encryption is applied correctly and the data remains encrypted throughout the relevant stages.
4. The Recipient Decrypts the Message
When the intended recipient receives the ciphertext, the decryption algorithm uses the appropriate key to reverse the encryption process.
With symmetric encryption, the recipient uses the same secret key used for encryption, or an equivalent copy of that key. With asymmetric encryption, the decryption key is mathematically related to the encryption key but is different from it.
If the correct key and required cryptographic parameters are available, the recipient can recover the original plaintext.
The entire process can happen almost instantly, allowing people to exchange messages securely without noticing the mathematical operations taking place behind the interface.
Symmetric Encryption: One Secret Key
Symmetric encryption uses a shared secret key to encrypt and decrypt information. Both parties must have access to the appropriate key, and that key must remain protected from unauthorized users.
This approach is widely used because it can encrypt large amounts of data efficiently.
Imagine that two people want to communicate privately. Before they begin exchanging encrypted messages, they need a way to establish the same secret key securely. Once they have it, the sender can encrypt a message, transmit the ciphertext, and allow the recipient to decrypt it with the shared key.
The main challenge is key distribution. If the secret key is intercepted during an insecure exchange, an attacker may be able to decrypt messages protected by that key.
Symmetric encryption is particularly useful for protecting files, databases, backups, network traffic, and the contents of messaging sessions.
How AES Protects Digital Information
One of the best-known symmetric encryption algorithms is the Advanced Encryption Standard, commonly called AES.
AES is a block cipher that processes data in fixed-size blocks of 128 bits. It supports key lengths of 128, 192, and 256 bits. Its design repeatedly transforms the data through mathematical operations that provide confusion and diffusion, making relationships between the plaintext, ciphertext, and key difficult to exploit.
AES is used in many applications, including secure communications, storage encryption, and wireless security systems.
However, AES alone does not describe an entire secure communication system. It must be used with an appropriate operating mode and correct implementation. Authenticated encryption modes, such as AES-GCM, can provide both confidentiality and integrity when their requirements are followed, including the correct handling of nonces.
A strong algorithm cannot compensate for a badly implemented system. Reusing a nonce where uniqueness is required, exposing secret keys, or incorrectly configuring encryption can undermine the protection AES is intended to provide.
Asymmetric Encryption: A Public Key and a Private Key

Symmetric encryption is efficient, but distributing a shared secret can be difficult when two people have never communicated before. Asymmetric cryptography helps solve this problem by using a pair of mathematically related keys.
The pair consists of a public key and a private key.
The public key can be shared openly. The private key must remain under the control of its owner.
In a traditional public-key encryption system, someone can encrypt information using the recipient’s public key. The corresponding private key is then needed to decrypt it.
This means the sender does not have to receive the recipient’s secret decryption key beforehand.
Public-key cryptography also supports digital signatures, which serve a different purpose. A digital signature allows others to verify that a message or document was signed using the corresponding private key and that the signed content has not been altered, assuming the system and verification process are trustworthy.
Encryption and digital signatures are related cryptographic technologies, but they should not be confused. Encryption protects confidentiality; digital signatures help establish authenticity and integrity.
Why Public-Key Cryptography Matters
Public-key cryptography makes secure communication between unfamiliar parties much more practical. It supports secure connections to websites, authenticated software updates, digital certificates, and various secure messaging systems.
Algorithms such as RSA have historically been important for public-key encryption and digital signatures. Elliptic-curve cryptography is also widely used in key agreement and digital signatures.
Different algorithms serve different purposes, and not every public-key algorithm is suitable for every cryptographic task. Modern protocols choose specific algorithms and combine them according to established security standards.
Public-key operations are generally more computationally expensive than symmetric encryption. For that reason, many systems use public-key cryptography to establish or authenticate a session key, then use symmetric encryption to protect the actual data.
This combination allows secure systems to benefit from the convenient key-management properties of public-key cryptography and the efficiency of symmetric encryption.
How Secure Messaging Combines Different Algorithms
Most modern secure communication systems do not depend on one encryption algorithm alone. They combine multiple cryptographic mechanisms, each designed to address a particular security problem.
Consider what happens when someone opens a secure website or sends a message through a properly designed encrypted messaging application.
First, the system establishes a secure cryptographic context. Depending on the protocol, the participants may authenticate identities, agree on shared secret material, and derive session keys.
Next, symmetric authenticated encryption protects the data exchanged during the session. The application may encrypt each message or record using the relevant session key and associated cryptographic parameters.
Finally, the recipient verifies the protected data and decrypts it. If authentication fails, a correctly implemented system should reject the altered or invalid data rather than silently treating it as trustworthy.
This layered approach helps solve several problems at once: establishing shared secrets, confirming identities, protecting message contents, and detecting unauthorized modification.
What Happens When You Send an Encrypted Message?
Consider a simplified example involving two friends, Maya and Daniel.
Maya writes a private message on her phone. Her messaging application uses cryptographic procedures to establish or access the appropriate encryption keys and protect the message. The resulting encrypted data travels through the service’s infrastructure.
A server may forward the ciphertext without needing to read the original message. Daniel’s device receives the encrypted data, verifies it where the protocol supports authentication, and decrypts it using the appropriate key.
If the application uses end-to-end encryption, the message is designed to remain readable only on the authorized endpoints, rather than by the messaging provider while it is in transit or stored on its servers. The exact guarantees depend on the application and its implementation.
This protection does not automatically cover everything associated with the conversation. Metadata, such as the time a message was sent or the accounts involved, may still be visible to the service. Notifications, cloud backups, compromised devices, and screenshots can also create separate privacy risks.
Encryption is therefore a critical part of secure messaging, but the complete privacy of a conversation depends on more than the encryption algorithm itself.
How Encryption Algorithms Prevent Unauthorized Access
A common misconception is that encrypted messages are impossible to break. In reality, their security depends on mathematical difficulty, key strength, correct implementation, and the capabilities of potential attackers.
Modern encryption algorithms are designed so that attempting to recover the plaintext without the necessary key would require an impractical amount of computation, assuming the algorithm is secure and correctly used.
Several principles contribute to this protection.
Large Key Spaces
The number of possible keys determines how many candidate keys an attacker might need to consider in a brute-force attack.
For a uniformly random key containing 128 bits, there are (2^{128}) possible key values. This is an enormous search space, making exhaustive key guessing infeasible with realistic computing resources when the algorithm and implementation are secure.
Longer keys can increase the search space, but key length alone does not guarantee security. The algorithm must be sound, the key must be generated properly, and the implementation must avoid exploitable weaknesses.
Resistance to Cryptanalysis
Cryptanalysis is the study of methods for analyzing and potentially breaking cryptographic systems.
Researchers investigate whether an algorithm leaks patterns, whether mathematical relationships can be exploited, and whether an attacker can recover information without testing every possible key.
Well-designed encryption algorithms undergo extensive public analysis. This scrutiny helps identify weaknesses before or during widespread deployment.
An algorithm that has resisted known attacks over many years may inspire greater confidence, although no amount of past analysis proves that a system can never be broken.
Secure Key Management
Even the strongest encryption algorithm becomes ineffective if an attacker obtains the secret key.
Keys can be exposed through malware, insecure storage, weak passwords, careless sharing, software vulnerabilities, or unauthorized access to a device.
For this reason, secure systems need procedures for generating, storing, rotating, and revoking keys. They may also use hardware security features to protect sensitive cryptographic material.
In many real-world incidents, attackers do not defeat the underlying encryption mathematics. Instead, they exploit weaknesses in the systems surrounding it.
Encryption Is Not the Same as Hashing

Encryption is sometimes confused with hashing, but the two technologies serve different purposes.
Encryption is designed to be reversible by someone who possesses the appropriate key. Hashing transforms input data into a fixed-length digest, and a secure cryptographic hash function is designed to make recovering the original input computationally impractical.
For example, websites commonly use password-hashing schemes to store password verifiers instead of storing users’ passwords in plaintext. When someone logs in, the system checks the submitted password against the stored verifier.
Secure password storage typically uses a purpose-built password-hashing algorithm, such as Argon2id, with an appropriate salt and carefully selected resource settings. Ordinary fast hashing alone is generally unsuitable for password storage because it allows attackers to test guesses too quickly.
Hash functions are also used in digital signatures, integrity checks, and other cryptographic applications.
The distinction is straightforward: encryption protects information that an authorized party needs to recover, while hashing supports verification and other operations that do not require reversing the transformation.
How Encryption Protects Online Banking and Shopping
Online banking and e-commerce depend on cryptographic technologies to protect sensitive information exchanged between devices and servers.
When a customer connects to a properly configured secure banking website, the connection commonly uses HTTPS, which relies on the Transport Layer Security (TLS) protocol.
TLS helps establish an authenticated, encrypted connection between the browser and the server. Certificates and related authentication mechanisms help the browser verify the server’s identity, while key agreement establishes the secrets used to protect the session.
After the secure connection is established, symmetric authenticated encryption protects the data exchanged over it.
This reduces the risk that someone monitoring the network can read or modify the protected traffic without detection. It is particularly important when customers access account information, submit payment details, or enter login credentials.
However, HTTPS does not guarantee that a website itself is honest. A fraudulent website can also use HTTPS. Users must still verify the website address and remain alert to phishing attempts.
Likewise, encryption cannot prevent every form of fraud. Criminals may trick customers into revealing authentication codes, steal passwords using malicious software, or exploit weaknesses in a bank’s own systems.
Cryptography protects data in specific ways; it does not eliminate every security risk associated with online transactions.
Can Quantum Computers Break Encryption?
The development of quantum computing has raised important questions about the long-term security of current cryptographic systems.
A sufficiently powerful, fault-tolerant quantum computer could use Shor’s algorithm to threaten widely used public-key cryptographic systems based on integer factorization and discrete logarithms, including RSA and many forms of elliptic-curve cryptography.
Such a computer could potentially undermine the mathematical assumptions that protect these systems.
Symmetric encryption faces a different situation. Grover’s algorithm could theoretically speed up brute-force searching, but it does not have the same effect on symmetric cryptography as Shor’s algorithm has on RSA or elliptic-curve systems. Increasing symmetric key sizes can help maintain appropriate security margins.
This is one reason the cybersecurity community is developing and adopting post-quantum cryptography: cryptographic algorithms designed to resist attacks from both conventional and quantum computers.
The U.S. National Institute of Standards and Technology (NIST) published its first finalized post-quantum cryptography standards in 2024, including standards for key establishment and digital signatures. Organizations are now working to integrate suitable post-quantum algorithms into their systems.
The transition will take time because cryptographic technologies are embedded in websites, applications, devices, networks, and long-lived stored information.
One concern is known as “harvest now, decrypt later.” An attacker might collect encrypted data today in the hope of decrypting it in the future if sufficiently powerful quantum computers become available. Information that must remain confidential for many years may therefore require particular attention during cryptographic planning.
Common Mistakes That Weaken Encryption
Encryption algorithms can be mathematically strong while the systems using them remain vulnerable. Several recurring mistakes can undermine their effectiveness.
Using weak passwords to protect encryption keys: If a key is derived from a weak password, attackers may be able to guess the password and recover the key. Secure password-based key derivation helps slow guessing attacks, but users must still choose strong passwords.
Reusing nonces incorrectly: Some encryption modes require nonces to be unique for each use of a given key. Violating this requirement can expose plaintext or compromise authentication, depending on the algorithm and mode.
Ignoring software updates: Security vulnerabilities can affect cryptographic libraries, operating systems, browsers, and applications. Updates help address known weaknesses.
Assuming encryption protects compromised devices: If malware or another attacker can access a message before it is encrypted or after it is decrypted, encryption in transit may not prevent exposure.
Failing to authenticate communication partners: Encryption without proper authentication may leave users vulnerable to impersonation or man-in-the-middle attacks. Secure protocols use certificates, authenticated key exchange, or other appropriate methods to reduce these risks.
Treating backups as automatically protected: An application may encrypt messages end to end but handle cloud backups differently. Users should check whether backups receive equivalent protection and who can access the relevant keys.
Avoiding these mistakes requires more than selecting a well-known algorithm. It requires careful design, secure implementation, sound key management, and ongoing maintenance.
The Future of Encryption Technology
Encryption continues to evolve as computers become more powerful, networks expand, and new security threats emerge.
Post-quantum cryptography is one important development. It aims to preserve secure communication even if future quantum computers undermine some currently used public-key algorithms.
Another area of development involves better key management, more secure hardware, and protocols that reduce the consequences of compromised keys. Researchers also continue to study methods that protect privacy while allowing certain forms of computation on sensitive data.
For example, homomorphic encryption can, in specific settings, allow computations to be performed directly on encrypted information without first decrypting it. This technology has potential applications in privacy-sensitive data processing, although it can be computationally expensive and is not a universal replacement for conventional encryption.
Other techniques, including secure multiparty computation and differential privacy, address related but distinct privacy challenges.
As digital communication becomes increasingly important, encryption will remain a central component of information security. Its continued effectiveness will depend on advances in mathematics, careful engineering, trustworthy implementations, and the ability of organizations to adapt as threats change.
Conclusion
Encryption algorithms keep messages secret by transforming readable information into ciphertext using carefully designed mathematical operations and cryptographic keys. Symmetric encryption provides efficient protection for large amounts of data, while asymmetric cryptography helps establish secure relationships between parties who do not already share a secret.
Modern communication systems combine these methods with authentication, integrity protection, and secure key management to protect messages, financial transactions, and other sensitive information.
Encryption is not an absolute guarantee of privacy, and its effectiveness can be undermined by weak passwords, compromised devices, implementation errors, or poor security practices. Nevertheless, when correctly designed and deployed, modern cryptography makes unauthorized access to protected information extraordinarily difficult.
From a private message on a smartphone to a financial transaction across the internet, encryption allows digital information to travel through complex networks while preserving confidentiality and helping people communicate with greater confidence.
Frequently Asked Questions
An encryption algorithm is a mathematical procedure that transforms readable information into ciphertext using a cryptographic key. An authorized recipient can recover the original information through the corresponding decryption process.
Symmetric encryption uses a shared secret key for encryption and decryption. Asymmetric cryptography uses a public key and a mathematically related private key, allowing certain security tasks to be performed without sharing the private key.
Yes. Encrypted messages can be intercepted or copied while traveling across a network. Proper encryption is designed to prevent an interceptor from understanding the message without the necessary key, although other vulnerabilities may still expose information.
AES remains a widely trusted encryption standard when used with suitable key sizes, appropriate modes, and correct implementations. Security also depends on proper nonce management, key protection, and the absence of weaknesses elsewhere in the system.
Encryption can protect message contents from attackers who intercept the data but lack the necessary keys. It cannot necessarily protect messages on a compromised device, prevent phishing, or stop an authorized recipient from sharing the information.
End-to-end encryption is a system in which messages are encrypted on the sender’s device and decrypted on the intended recipient’s device. When implemented correctly, the service provider cannot read the message contents merely by accessing the encrypted data stored or transmitted through its infrastructure.
No. Quantum computers pose significant potential threats to some public-key cryptographic algorithms, but they do not make all encryption useless. Post-quantum cryptographic standards and appropriate symmetric key sizes are among the measures being developed to address future risks.


One thought on “How Encryption Algorithms Keep Messages Secret”